This page describes what is architecturally true. Formal certification status is listed at the bottom, unembellished.
You can read the payload before we ever see it.
The strongest privacy claim we can make is not a policy, it is that the SDK never reads your prompts, and that you can verify exactly what would be sent from your own machine before a byte leaves it.
There is no setting that turns prompt capture on, because the SDK never reads them.
Verify it yourself, first.
Set AGENTSIGHT_FILE_EXPORTER and spans are written to a directory instead of being transmitted. Run your own application against your own traffic, open the files, and read the exact payload that would have been sent.
Most vendors ask you to trust a policy page. This is the same claim, checkable in an afternoon, before you send us anything.
- provider
- "openai"
- requested_model
- "gpt-4o"
- resolved_model
- "gpt-4o-2024-08-06"
- input_tokens
- 1284
- output_tokens
- 312
- cache_read_tokens
- 1024
- operation
- "chat"
- streaming
- true
- duration_ms
- 700
- status
- "ok"
Never transmitted
- prompt
- completion
- messages[]
- system
LLM spans carry the accounting only. There is no setting that turns prompt capture on, because the SDK never reads them.
What is recorded, and who can reach it.
| Control | Behaviour |
|---|---|
| What leaves your machine | |
| Model call accounting | Token counts, model ids and timings only. Prompt and completion text is never read by the SDK. |
| Message content | Only what you explicitly record with user_message() and agent_message(). |
| Tool arguments and responses | Recorded, truncated at 16,384 characters. |
| Personal data | Only the fields you pass, customer id, IP, device, language. |
| Credentials | |
| API keys | ags_ prefix, scoped read-only or full, per agent, revocable, with expiry. |
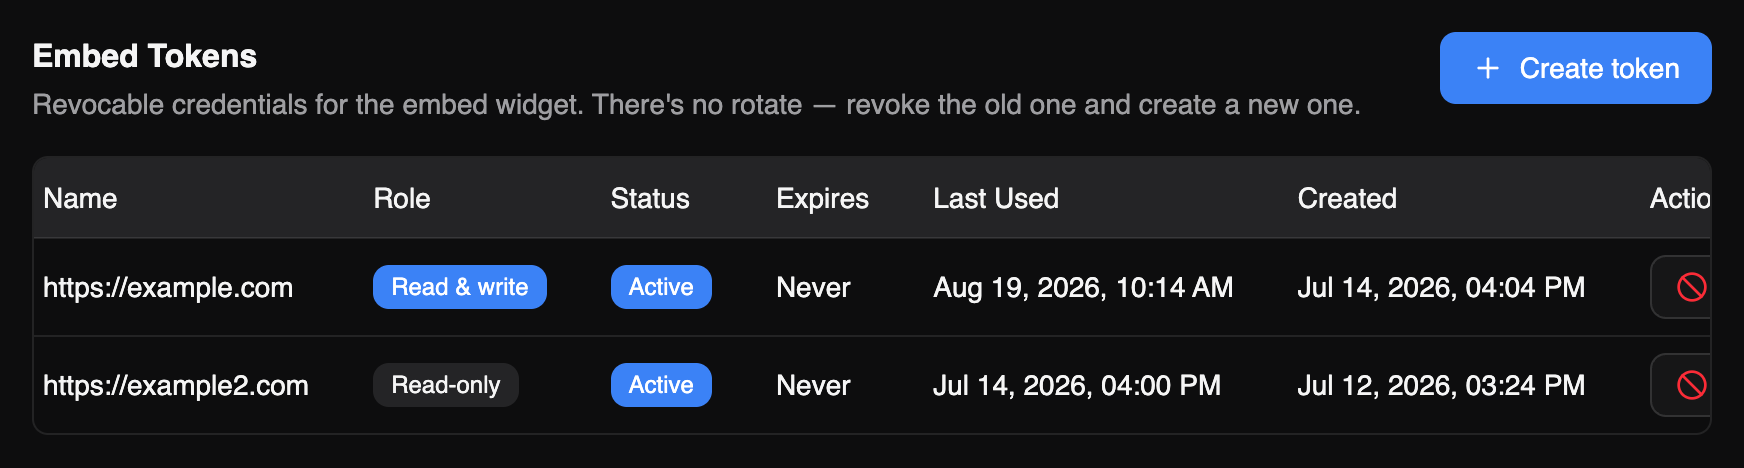
| Embed tokens | agse_ prefix, read-only or read-write, revocable, with expiry and last-used tracking. |
| Origin allow-list | Re-checked on every request, not cached at token creation. |
| Access | |
| Roles | Owner, Editor, Viewer, enforced at the route, not hidden in the UI. |
| Invitations | Pending, accepted or rejected, with an audit of ownership transfer. |
| Subdomain field flags | Eight per-conversation fields you can hide from a client. |
| Embed PII defaults | Off, because an embed has no per-individual login. |
We would rather show an honest gap here than a badge we have not earned.
Certification status.
In progressWe are not going to print compliance logos we do not hold. Formal certification is being worked through; data region, retention policy and DPA availability are being documented alongside it.
If your procurement process needs specifics before that lands, ask us directly and you will get a straight answer about where we actually are.
Security and privacy questions.
Do you read our prompts?
No. Model spans carry provider, model ids, token counts, timings and status. Prompt and completion text is never read by the SDK, so there is nothing to transmit.
Can we see what would be sent?
Yes, AGENTSIGHT_FILE_EXPORTER writes spans to a directory instead of transmitting them. Inspect the files before you point the SDK at us.
What if a token leaks?
Revoke it; it stops immediately. Embed tokens are also bound to an origin allow-list re-checked on every request, so a leaked token is useless from an unlisted domain.
Can a client see other clients' data?
No. Everything, agents, tokens, flags, roles, is scoped per agent, and route-level enforcement means guessing a URL does not work.
Where is the data stored?
Data region is a field on the agent profile and the specifics are being documented as part of the compliance work above. Ask us and we will tell you exactly where you would sit.
Check the payload before you trust the policy.
- Full dashboard on the free plan
- No card required
- Model spans never carry prompts